Agentic AI Identity
Identity Authority and Trust
Identity-first consulting for agentic AI.
Secure every AI agent with an identity of its own.
AI agents are already at work inside your environment, calling APIs, moving data, and making decisions using credentials that belong to people. We help you give every agent its own identity, its own scope, and its own audit trail, built on the IAM stack you already trust.
We specialize in one thing: securing AI agents with identity. Not a bolt-on product pitch, but a discipline built on the identity and access management foundation your enterprise already runs. Every agent that acts inside your organization deserves an identity of its own, scoped authority, and an audit trail you can defend. We make that real.
Agent identity strategy
We define what an agent identity means for your organization (attributes, owners, lifecycle, and trust) and map it to the identity platform you already run.
Delegation & consent design
Agents act for people, but never as people. We design delegation models so every action carries limited, explicit, revocable authority.
Policy & governance
One policy engine governing every agent: least-privilege scopes, continuous auditing, and instant revocation without reviewing actions by hand.
Readiness assessment
A focused engagement that places your agent estate on our four-stage maturity model and hands you a prioritized, executive-ready roadmap.
Our Consulting Approach
Engaging us means getting advice that survives contact with your environment, from consultants who have run identity programs at enterprise scale.
Vendor neutral guidance
We work with the IAM investment you already have, whether that's Entra, Okta, Ping, CyberArk, or any mix, and recommend only what your environment actually needs.
Standards-based architecture
Patterns grounded in emerging standards like SPIFFE/SPIRE for workload identity and WIMSE for agent-to-agent trust, so your design doesn't lock you into one vendor.
Hands-on with your teams
Working sessions with your security, identity, and platform teams, not a deck left behind. Your people finish the engagement able to run agent identity themselves.
A plan you can defend
Every engagement ends with a prioritized roadmap your CISO can take to the board: what to fix first, why, and what it costs to leave it unfixed.
Our Engagement Model
A proven four-stage engagement that takes you from unknown agent risk to governed agent identity, without a rip-and-replace of anything you already own.
01
Access
We inventory every agent in your environment (what credentials it uses, what it can reach, and who it answers to) and score you against our four-stage readiness model.
02
Design
We architect the agent identity model for your stack: identity issuance, scoped authority, delegation and consent, and the policy layer that governs it all.
03
Implement
Alongside your teams, we roll out agent identities in controlled waves, starting with your highest-risk agents, with least-privilege scopes and full audit trails from day one.
04
Govern
We hand over the controls that scale: continuous auditing, drift detection, instant revocation, and the operating model to onboard every new agent the same way.
Most engagements begin with a two-week readiness assessment.
The Six Part Series
A Guided Path From Unmanaged Agents to Governed Identity.
Our thinking in depth. Each part of the series tackles one question your security and identity teams will face as agents multiply across the enterprise. Read it before you talk to us, or after; it’s the same philosophy we bring to every engagement.
01
Agents Already Have Identities; Nobody Issued Them
AI agents are already calling APIs, moving data, and making decisions using credentials that belong to people. The problem isn't that agents lack access; it's that nobody issued them an identity of their own, so every action is attributed to a human who wasn't there.
02
What an Agent Identity Actually Needs
An agent identity is more than a service account: verifiable attributes, a defined owner, scoped authority, and a full lifecycle to issue, rotate, and revoke. Emerging standards like SPIFFE/SPIRE for workload identity and WIMSE for agent-to-agent trust provide the rails to do this natively in your existing stack.
03
Acting on Your Behalf, Not as You
When an agent acts for a user, it must never simply become that user. We design delegation and consent models so every action carries limited, explicit authority: what the agent may do, on whose behalf, and for how long.
04
How Agent Identity Fails
Token leakage, standing permissions that were never scoped down, and agent-to-agent delegation chains that quietly expand authority. Understanding these failure modes is the first step toward controls that catch them.
05
Policy Is the Control That Scales
You can't review every agent action by hand. Policy-based authorization, continuous auditing, and instant revocation let you govern thousands of agents with the IAM investment you already run: one policy engine, every agent.
06
Where You Are and Where to Go Next
The series closes with a simple readiness model that places your current agent systems on a maturity scale and maps the concrete next steps to governed, auditable agent identity, without a rip-and-replace.
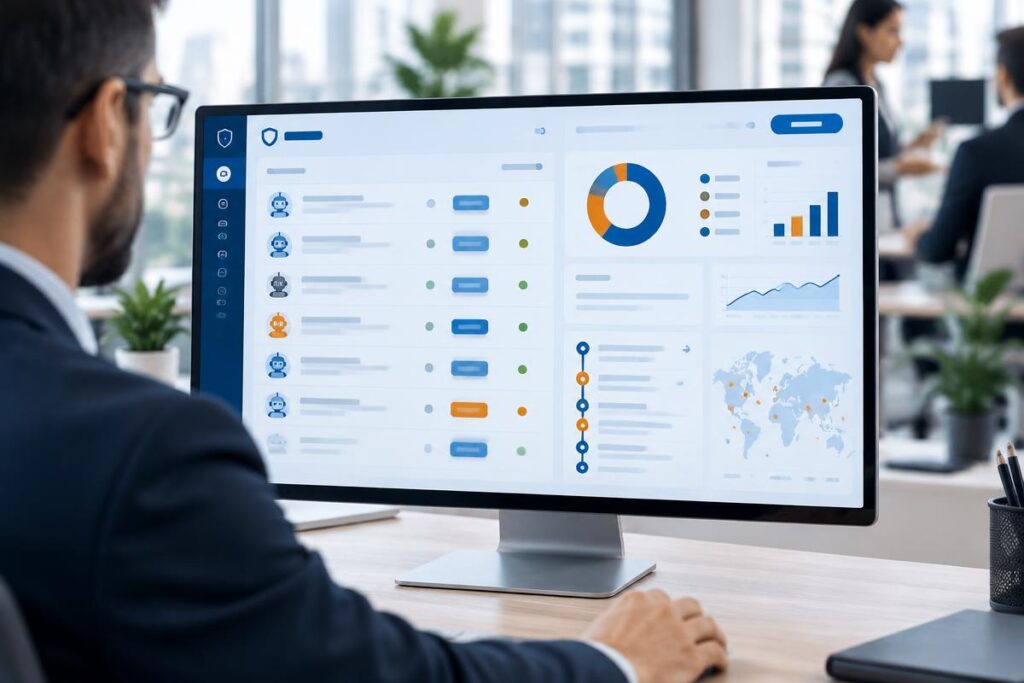
A short assessment places your agent estate on a four-stage readiness scale and maps the concrete next moves to reach governed agent identity on your existing stack.
Let’s Talk About Your Needs
Please Fill Out the Form Below to Let Us Know What We Can Do for You. We Will Get Back to You at the Earliest.